// Service
Networks, VPNs & firewalls
Connect offices, servers and cloud securely, split your network into sensible zones, and know what is happening on it. Designed simply, documented clearly, monitored continuously.
Building and interconnecting VPNs
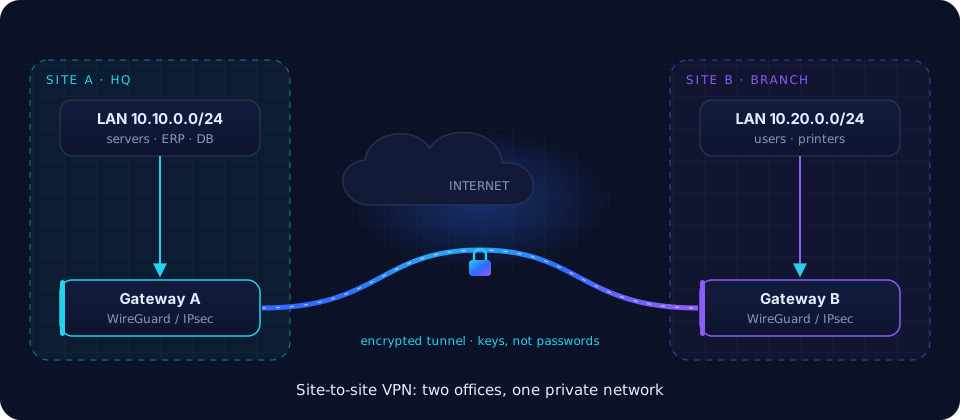
Whether you need two offices on one private network, remote staff reaching internal systems, or a secure link to the cloud, we design and build VPNs that are fast, simple to operate and based on keys, not shared passwords.
- Site-to-site VPNPermanent encrypted tunnels between offices, data centres and cloud networks (OCI, AWS, Azure).
- WireGuardModern, lean and fast. Our default for new Linux-based links and remote access.
- IPsec (IKEv2)For interoperability with existing firewalls, routers and cloud VPN gateways.
- Remote accessPer-user keys, revocable at any time, with access only to what each person needs.
Network layout design
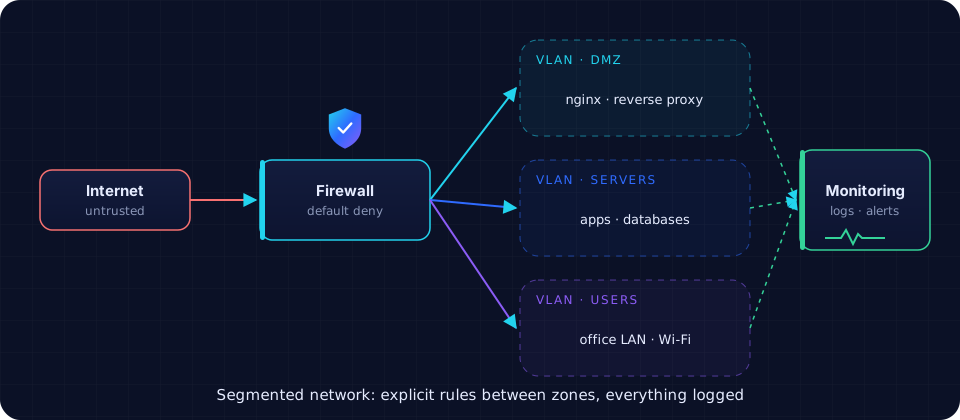
Flat networks where every device can reach every other are the easiest place for an attacker to spread. We design a layout that fits your size: separate zones (VLANs) for servers, users, guests, a DMZ for public services and management, with clear addressing and documentation.
Firewalls with security and monitoring first
- Default denyOnly explicitly allowed traffic passes between zones and to the internet. Rules are reviewed and documented.
- Hardeningnftables/firewalld on Linux, or your existing firewall appliance; minimal exposed services, rate limiting, geo and brute-force protection.
- Monitoring & loggingCentral logs, alerts for unusual traffic, tunnel and link health checks, certificate and uptime monitoring.
- Regular reviewsPeriodic rule clean-up and a short report: what changed, what was blocked, what needs attention.
Frequently asked questions
WireGuard or IPsec: which should we use?
WireGuard for new links between Linux systems and for remote access: it is simpler and faster. IPsec when one side is an existing firewall or cloud gateway that only speaks IPsec. Both can coexist.
Can you connect our office to our cloud servers?
Yes. We build site-to-site VPNs to OCI, AWS and Azure, either to their managed VPN gateways or to a small Linux gateway you control.
Do we need expensive hardware firewalls?
Not necessarily. For many small and mid-size networks a well-configured Linux firewall or the device you already own is enough. We recommend hardware only when it clearly pays off.